In today's digital landscape, where cyber threats are becoming increasingly sophisticated, organizations must prioritize employee trainingemployee training to safeguard their sensitive information. One of the most effective methods to prepare staff for these challenges is through phishing simulationsphishing simulations. These simulations mimic real-world phishing attacks, allowing employees to experience firsthand how to identify and respond to such threats. But why are these simulations crucial in the realm of cybersecurity best practices? As cybercriminals refine their tactics, even the most vigilant employees can fall prey to deceptive emails or messages.
The consequences of a successful phishing attack can be devastating, leading to data breaches, financial loss, and reputational damage. This is where phishing simulations for employee training come into play. By creating a safe environment for employees to learn, organizations can transform their workforce into a robust line of defense against cyber threats. This article will delve into the importance of phishing simulations in enhancing employee awareness, the mechanics behind these training programs, and the tangible benefits they offer to organizations committed to fostering a culture of cybersecurity. Join us as we explore how implementing effective phishing simulations can not only reduce vulnerability but also empower employees with the knowledge and skills needed to combat phishing attacks effectively. The rise of phishing attacks has become a significant concern for organizations worldwide.
These attacks exploit human psychology to trick employees into revealing sensitive information, leading to severe data breaches and financial losses. As cybercriminals continuously refine their tactics, it is essential for businesses to implement effective training programs that equip employees with the knowledge needed to recognize and respond to phishing attempts. This is where phishing simulations come into play.
Phishing simulations
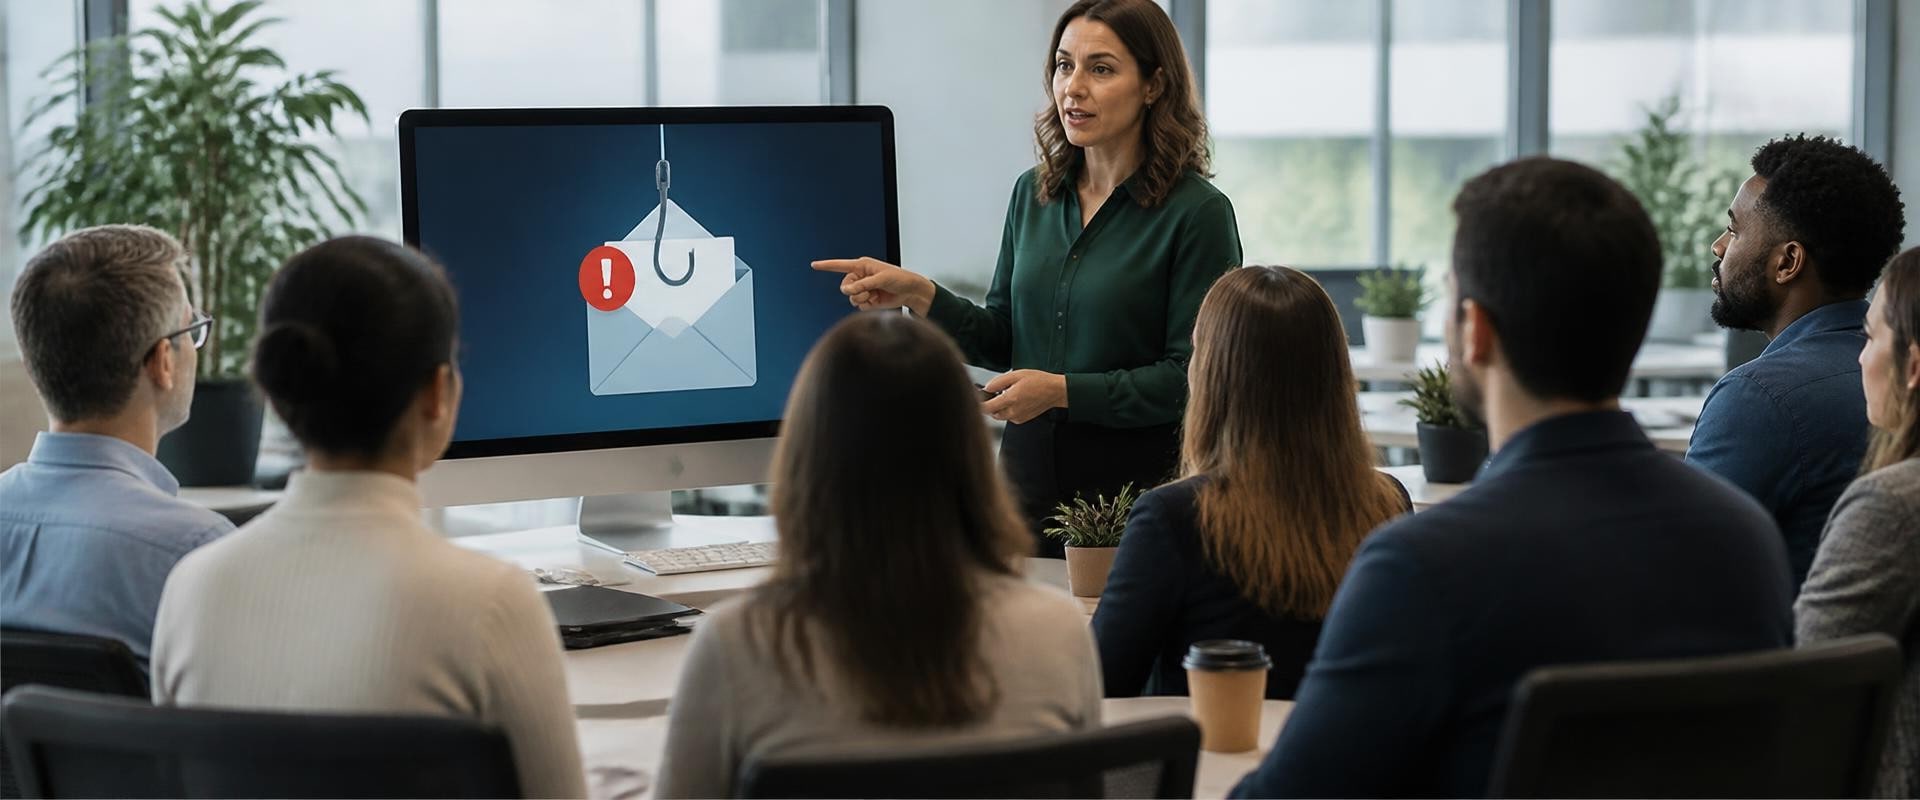
are controlled exercises designed to mimic real phishing attacks. They help organizations train their employees by creating a safe environment where individuals can learn to identify various types of phishing attempts without the risk of actual data loss or breach.These simulations can replicate a range of phishing techniques, including email phishing, which is the most common form, as well as SMS phishing (or smishing), voice phishing (vishing), and even social media phishing. By exposing employees to these different scenarios, organizations can assess their readiness and reinforce best practices for recognizing suspicious communication. Successful implementations of phishing simulations can lead to significant improvements in employee awareness and response rates. For example, a leading financial institution conducted a series of simulations over six months, targeting their entire workforce with various phishing scenarios. Initially, approximately 30% of employees fell victim to these simulated attacks.
However, after completing the training program that included feedback on the simulations, that number dropped to just 10%. This dramatic shift highlights the effectiveness of such training programs in enhancing employee vigilance against real threats. Statistics underscore the positive impact of phishing simulations. According to recent studies, organizations that implemented regular phishing simulation exercises reported a 70% reduction in successful phishing attempts within a year. Furthermore, employees who participated in these training sessions demonstrated a marked improvement in their ability to identify suspicious emails and URLs.
Before the training, only 45% of employees could correctly identify fraudulent messages; after the training, that figure soared to 85%. These numbers illustrate not just an increase in awareness but also a tangible shift in behavior that is crucial for maintaining organizational security. Despite these successes, some common objections and misconceptions persist regarding the effectiveness of phishing simulations. One prevalent concern is that employees may feel demoralized or mistrusted if they are subjected to simulated attacks. However, well-designed programs emphasize learning and growth rather than punishment.
Feedback should be constructive, focusing on areas for improvement rather than placing blame. Moreover, when employees understand that these simulations are implemented for their protection and the organization's overall security, they are more likely to engage positively with the training process. Another misconception is that one-off training sessions are sufficient to combat evolving threats. In reality, continuous training and assessment are critical components of an effective cybersecurity strategy. Cyber threats are constantly evolving; therefore, regular updates to training content and frequent simulations ensure that employees remain vigilant and informed about the latest tactics used by cybercriminals.
Companies should aim for an ongoing culture of security awareness that reinforces best practices and keeps employees engaged with new learning materials. In conclusion, phishing simulations are an indispensable tool in the fight against cyber threats. By providing employees with practical experience in identifying phishing attempts, organizations can significantly reduce their vulnerability to these attacks. The success stories and statistical evidence demonstrate that investing in employee training through simulations not only enhances security but also fosters a proactive approach to cybersecurity across the organization.
What Are Phishing Simulations?
Phishing simulations are practical exercises designed to replicate real-world phishing attacks in a controlled environment. Their primary purpose is to assess and enhance the cybersecurity awareness of employees within an organization.By mimicking the tactics used by cybercriminals, these simulations enable companies to identify vulnerabilities in their workforce's ability to recognize and respond to phishing attempts. The role of phishing simulations in cybersecurity training is crucial. They provide a hands-on learning experience that goes beyond traditional training methods. Employees can engage with realistic scenarios where they must detect and report suspicious emails or messages. This interactive approach not only improves their skills but also fosters a culture of vigilance and responsibility regarding cybersecurity. Moreover, the data collected from these simulations can help organizations tailor their training programs more effectively.
By analyzing employee responses, companies can pinpoint areas where additional training is needed, ensuring that resources are allocated efficiently to combat the ever-evolving threat of phishing attacks.
The Future of Phishing Simulations
As organizations increasingly recognize the importance of phishing simulations for employee training, the technology behind these simulations is evolving rapidly. One significant trend is the integration of artificial intelligence and machine learning, which enhances the realism and effectiveness of phishing scenarios. By analyzing user behavior and interaction patterns, AI-driven simulations can create more targeted and personalized phishing attacks that reflect the latest tactics employed by cybercriminals. Another advancement is the use of virtual reality (VR) and augmented reality (AR) technologies in phishing simulations. These immersive environments can provide employees with a more engaging training experience, allowing them to practice identifying phishing attempts in realistic settings.Such interactive training methods are likely to improve retention rates and prepare employees to respond effectively to actual threats. Furthermore, as remote work continues to be a staple for many organizations, phishing simulation platforms are adapting to address the unique challenges posed by remote environments. This includes designing simulations that mimic phishing attempts specifically targeting remote workers, such as emails that leverage home office themes or telecommuting tools. Lastly, we can expect advancements in analytics and reporting capabilities within phishing simulation tools. Organizations will benefit from detailed insights into employee performance, allowing them to tailor their training programs based on individual weaknesses and overall team vulnerabilities. This data-driven approach will enable businesses to refine their cybersecurity strategies continuously. In summary, the future of phishing simulations looks promising, with innovations aimed at creating more effective and engaging training experiences.
As cyber threats continue to evolve, so too must our approaches to employee education and awareness.
Measuring Success: Key Metrics
To effectively gauge the success of phishing simulations for employee training, organizations should focus on several key metrics that provide insights into employee awareness and behavior. These metrics not only help in assessing the current state of cybersecurity awareness but also in identifying areas that require further training and improvement.1.Click-Through Rate (CTR)
: This metric measures the percentage of employees who click on phishing simulation emails. A high CTR indicates a lack of awareness, while a low CTR suggests that employees are becoming more vigilant. Tracking this rate over time can illustrate the effectiveness of training programs.2.Reporting Rate
: Encouraging employees to report suspicious emails is a critical component of a strong security culture.The reporting rate measures how many employees report phishing attempts, whether real or simulated. An increase in this metric can indicate that employees are becoming more proactive and aware of potential threats.3.
Training Completion Rate
: This metric tracks the percentage of employees who complete phishing awareness training after undergoing simulations. A high completion rate suggests that employees are engaging with the training material, which is essential for fostering a culture of cybersecurity awareness.4.Post-Training Assessment Scores
: After conducting phishing simulations, organizations should evaluate employees through assessments or quizzes. Analyzing post-training scores can help determine how well employees understood the material and if they can identify phishing attempts effectively.5.Time to Report
: Measuring how quickly employees report phishing attempts can also provide insight into their level of awareness.A shorter time to report indicates that employees are not only recognizing threats but are also acting on them promptly. By consistently monitoring these metrics, organizations can refine their phishing simulation programs, tailor training efforts, and ultimately strengthen their defenses against phishing attacks.
Benefits of Implementing Simulations
Phishing simulations are an essential component of employee training programs aimed at combating the rising threat of phishing attacks. By engaging employees in realistic scenarios, organizations can significantly enhance their security posture. Here are some key advantages of implementing these simulations:1.Realistic Experience: Phishing simulations provide employees with a hands-on experience that mimics actual phishing attempts. This realistic exposure helps them recognize the signs of phishing emails and develop a more intuitive understanding of potential threats.2.Increased Awareness:
Regularly conducting phishing simulations raises awareness among employees about the prevalence and tactics used in phishing attacks.This heightened awareness fosters a culture of vigilance, making employees more likely to report suspicious communications.
3.Behavior Modification:
Through repeated exposure to phishing scenarios, employees can modify their behavior and improve their decision-making skills when faced with real threats. This change in behavior can lead to a significant reduction in successful phishing attempts.4.Immediate Feedback:
Simulations provide immediate feedback to employees, allowing them to learn from their mistakes in a safe environment. This instant feedback loop is crucial for reinforcing learning and ensuring that employees understand what they did wrong.5.Tailored Training:
Organizations can customize phishing simulations to target specific vulnerabilities within their workforce. By analyzing results, companies can identify areas that require additional training and focus on those aspects to strengthen their defenses.6.Measuring Effectiveness:
Implementing phishing simulations allows organizations to measure the effectiveness of their employee training programs.By tracking metrics such as click rates and reporting rates, companies can gauge improvements over time and adjust their training strategies accordingly. In conclusion, the benefits of using phishing simulations in employee training extend beyond immediate risk reduction; they contribute to building a robust cybersecurity culture within the organization. By investing in these simulations, businesses can empower their employees to become the first line of defense against cyber threats.
Types of Phishing Attacks Covered
Phishing attacks come in various forms, each with unique tactics designed to deceive individuals and gain unauthorized access to sensitive information. Understanding these types is crucial for developing effective phishing simulations for employee training. Below are some of the most common types of phishing attacks that can be simulated in training programs:Email Phishing: This is the most prevalent form of phishing, where attackers send fraudulent emails that appear to be from reputable sources.These emails often contain malicious links or attachments that, when clicked, can compromise an employee's credentials or install malware on their device.
Spear Phishing
: Unlike general email phishing, spear phishing targets specific individuals or organizations. Attackers gather personal information about their victims to craft highly personalized messages, making it more likely that the recipient will fall for the deception.Whaling
: This type of phishing is a form of spear phishing that specifically targets high-profile individuals within an organization, such as executives or senior management. Whaling attacks often mimic legitimate business communications and exploit the authority of the targeted individual.Vishing
(Voice Phishing): Vishing involves phone calls instead of emails. Attackers may pose as legitimate representatives from trusted organizations to extract sensitive information from employees over the phone.Smishing
: Similar to vishing, smishing uses SMS text messages to deceive recipients into revealing personal information or clicking on malicious links.With the increasing use of mobile devices, smishing has become a significant concern.
Clone Phishing
: In this attack, a legitimate email that has previously been sent to the victim is duplicated and altered to include a malicious link or attachment. The attacker then sends this cloned email, hoping the victim will trust it due to its familiar appearance.Business Email Compromise (BEC)
: This sophisticated scam targets businesses working with foreign suppliers and companies that regularly perform wire transfer payments. Attackers impersonate a company executive or vendor and trick employees into transferring funds or providing sensitive data. By simulating these various types of phishing attacks, organizations can equip their employees with the skills and knowledge needed to recognize and respond effectively to potential threats. This proactive approach helps to create a culture of cybersecurity awareness and significantly reduces the risk of successful phishing attempts.Best Practices for Conducting Phishing Simulations
Implementing effective phishing simulations is crucial for enhancing employee awareness and resilience against real phishing attacks.Here are some best practices to consider:1.Tailor Simulations to Your Organization: Understand the specific threats your organization faces and customize simulations accordingly. Utilize scenarios that reflect the types of phishing attacks relevant to your industry.
2.Start with a Baseline Assessment:
Before conducting simulations, assess your employees' current awareness levels through a preliminary test. This will help you gauge the effectiveness of your training programs over time.3.Use Realistic Scenarios:
Create simulations that mimic real-life phishing attempts. Incorporate elements such as familiar sender names, relevant content, and urgent calls to action to increase the realism of the scenarios.4.Educate Before You Execute:
Provide initial training on recognizing phishing attempts before launching simulations.This helps employees understand what to look for and reduces feelings of frustration or embarrassment if they fall for a simulated attack.
5.Analyze Results Thoroughly:
After each simulation, analyze the results to identify patterns in employee responses. Look for common mistakes and areas where additional training may be needed.6.Provide Immediate Feedback:
Following a simulation, offer immediate feedback to participants. If an employee clicks on a simulated phishing link, provide them with information on what they missed and how to improve in the future.7.Foster a Positive Learning Environment:
Encourage open discussions about mistakes made during simulations. Create a culture where employees feel safe to report phishing attempts without fear of punishment.8.Regularly Update Simulations:
Continuously update your phishing simulations to reflect evolving threats and tactics used by cybercriminals.This ensures that training remains relevant and effective.
9.Involve Management:
Get buy-in from leadership for your simulation program. When management participates or promotes awareness, it reinforces the importance of security throughout the organization.10. Measure Long-Term Impact:
Conduct follow-up assessments periodically to measure improvements in employee awareness and response rates over time. Adjust training and simulation strategies based on these insights. In conclusion, phishing simulations for employee training are a crucial element in defending organizations against the ever-evolving landscape of cyber threats. As we have discussed, the rise of sophisticated phishing attacks has led to significant data breaches, underscoring the urgent need for comprehensive employee training programs.By implementing phishing simulations, organizations can effectively prepare their staff to recognize and respond to these threats. Through the exploration of various types of phishing attacks, the benefits of simulations, and best practices for execution, it is clear that proactive measures are essential in fostering a culture of cybersecurity awareness. Additionally, measuring success through key metrics allows organizations to refine their training approaches and ensure maximum effectiveness. As phishing tactics continue to evolve, it is imperative for organizations to remain vigilant and adapt their training programs accordingly. Investing in phishing simulations not only protects sensitive information but also empowers employees to become the first line of defense against cybercriminals. Now is the time for organizations to prioritize these initiatives and safeguard their digital environments.